
Nobody has brought it up in conversation, here in iceland. Not one customer, not one prospect, not one founder in the room at a startup event. The EU AI Act is months away from reshaping how AI products are built, deployed, and sold into regulated markets, and the silence on the ground is deafening.
That silence is the data point. And it raises a question we at Sinope are genuinely putting to the community: how are companies actually preparing, and are they even sure which standard applies to them?
The Framework Confusion Is Real
Here is where it gets interesting. Talk to people in the industry and you will hear ISO 27001 and ISO 27002 come up frequently. Both are serious, well-established standards. ISO 27001 is an information security management system. ISO 27002 is a controls framework that sits alongside it. Both matter. Neither was designed with artificial intelligence in mind.
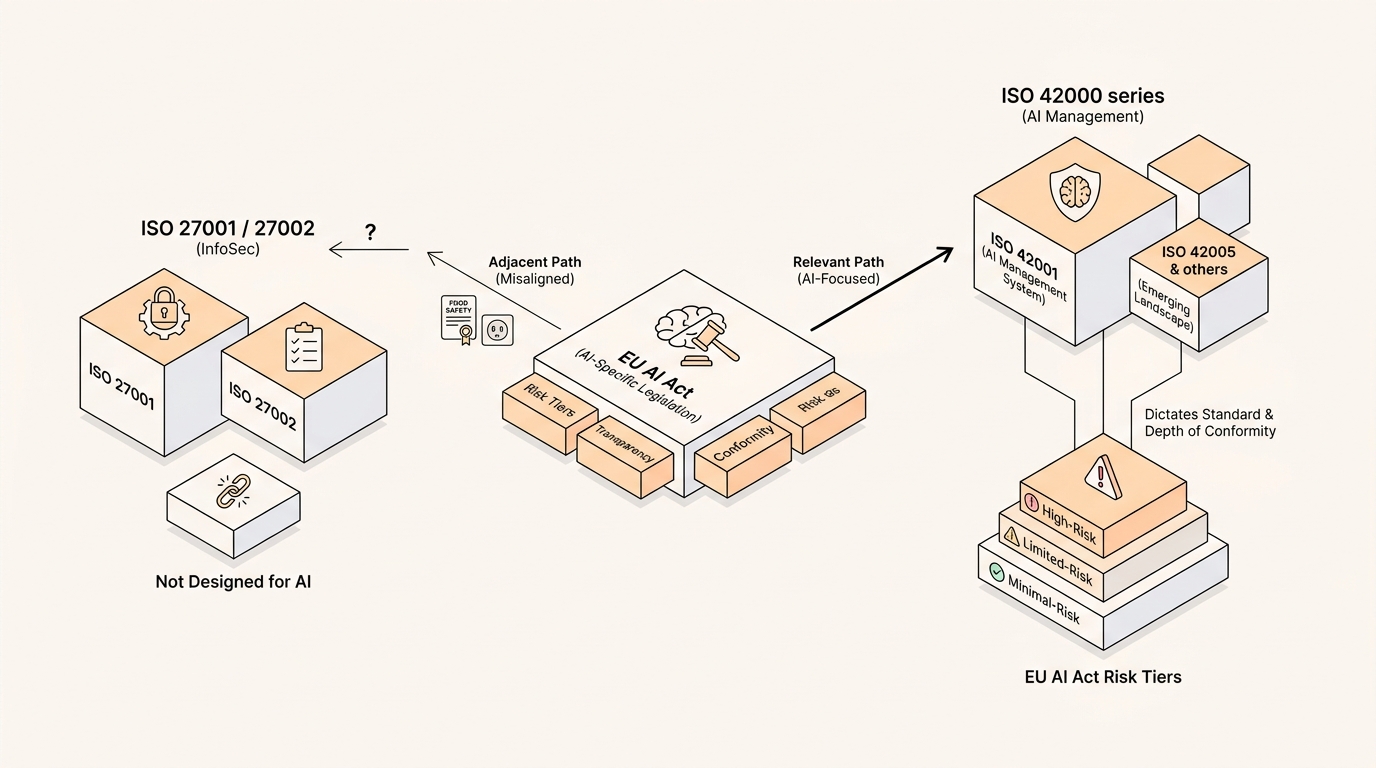
The EU AI Act is AI-specific legislation. It introduces risk tiers, transparency obligations, and conformity requirements that did not exist before. Reaching for ISO 27001 or ISO 27002 as your primary compliance path for an AI product is a bit like filing a food safety certificate when the inspector is coming to check your electrical wiring. Adjacent, but not the same thing.
The standards that look directly relevant are in the ISO 42000 series. ISO 42001 is the one generating the most attention: Information Technology, Artificial Intelligence Management System. There are others in that family, including ISO 42005, and the landscape is still taking shape. Which one applies to your situation depends on what you are building, who you are selling to, and where your product lands on the EU AI Act's risk tier classification.
That last part matters more than most people realize. High-risk AI systems, think hiring tools, credit scoring, biometric identification, face a much heavier compliance burden than limited-risk or minimal-risk systems. The standard you pursue, and the depth of conformity you need to demonstrate, should follow from that classification first.
Where Sinope Sits in This
We will be honest about our own position here, because we think transparency is more useful than authority posturing.

We are in the business of compliance. Sinope exists to help founders get into regulated markets without pausing their roadmap for six months. We use our own software to prove our own certifications, which means we cannot offer something to customers that we have not validated ourselves. That is the standard we hold ourselves to.
And right now, we are navigating the same question our customers are: which of these standards does Sinope need to hold internally, and which ones do we build into the product to help customers achieve? ISO 42001 looks like the most directly relevant starting point for AI management. But the 42000 series is still maturing, and the right answer for Sinope is probably not the same as the right answer for every customer we work with.
The honest position is that we are figuring this out in real time, the same as everyone else. What we are not doing is waiting.
What We Want to Know
The EU AI Act is not hypothetical. It is law. And the compliance path for AI-native products is not yet well-worn in the way that ISO 27001 has been for software companies over the past decade.

So here is the question, put plainly: what are you doing to prepare?
Are you treating ISO 27001 as sufficient coverage and hoping it holds? Are you going after ISO 42001 specifically? Are you waiting to see how enforcement shapes up before committing to a path? And does your answer change depending on where your product sits on the risk tier spectrum?
We are not asking rhetorically. The conversation is genuinely useful to us, and we suspect it is useful to anyone else building an AI product who has been quietly wondering whether they are the only one who has not figured this out yet.
The silence in Iceland might be an outlier. It might be a leading indicator. Either way, it is worth breaking.